 IntuneBrew
Vulnerabilities
Find the apps on your Macs with known vulnerabilities, including actively exploited ones, and update them.
IntuneBrew checks every catalog app daily against the NIST National Vulnerability Database (CVEs) and the CISA list of Known Exploited Vulnerabilities (KEV). The Vulnerabilities page in the portal matches that data against the app versions Intune detected on your Macs.
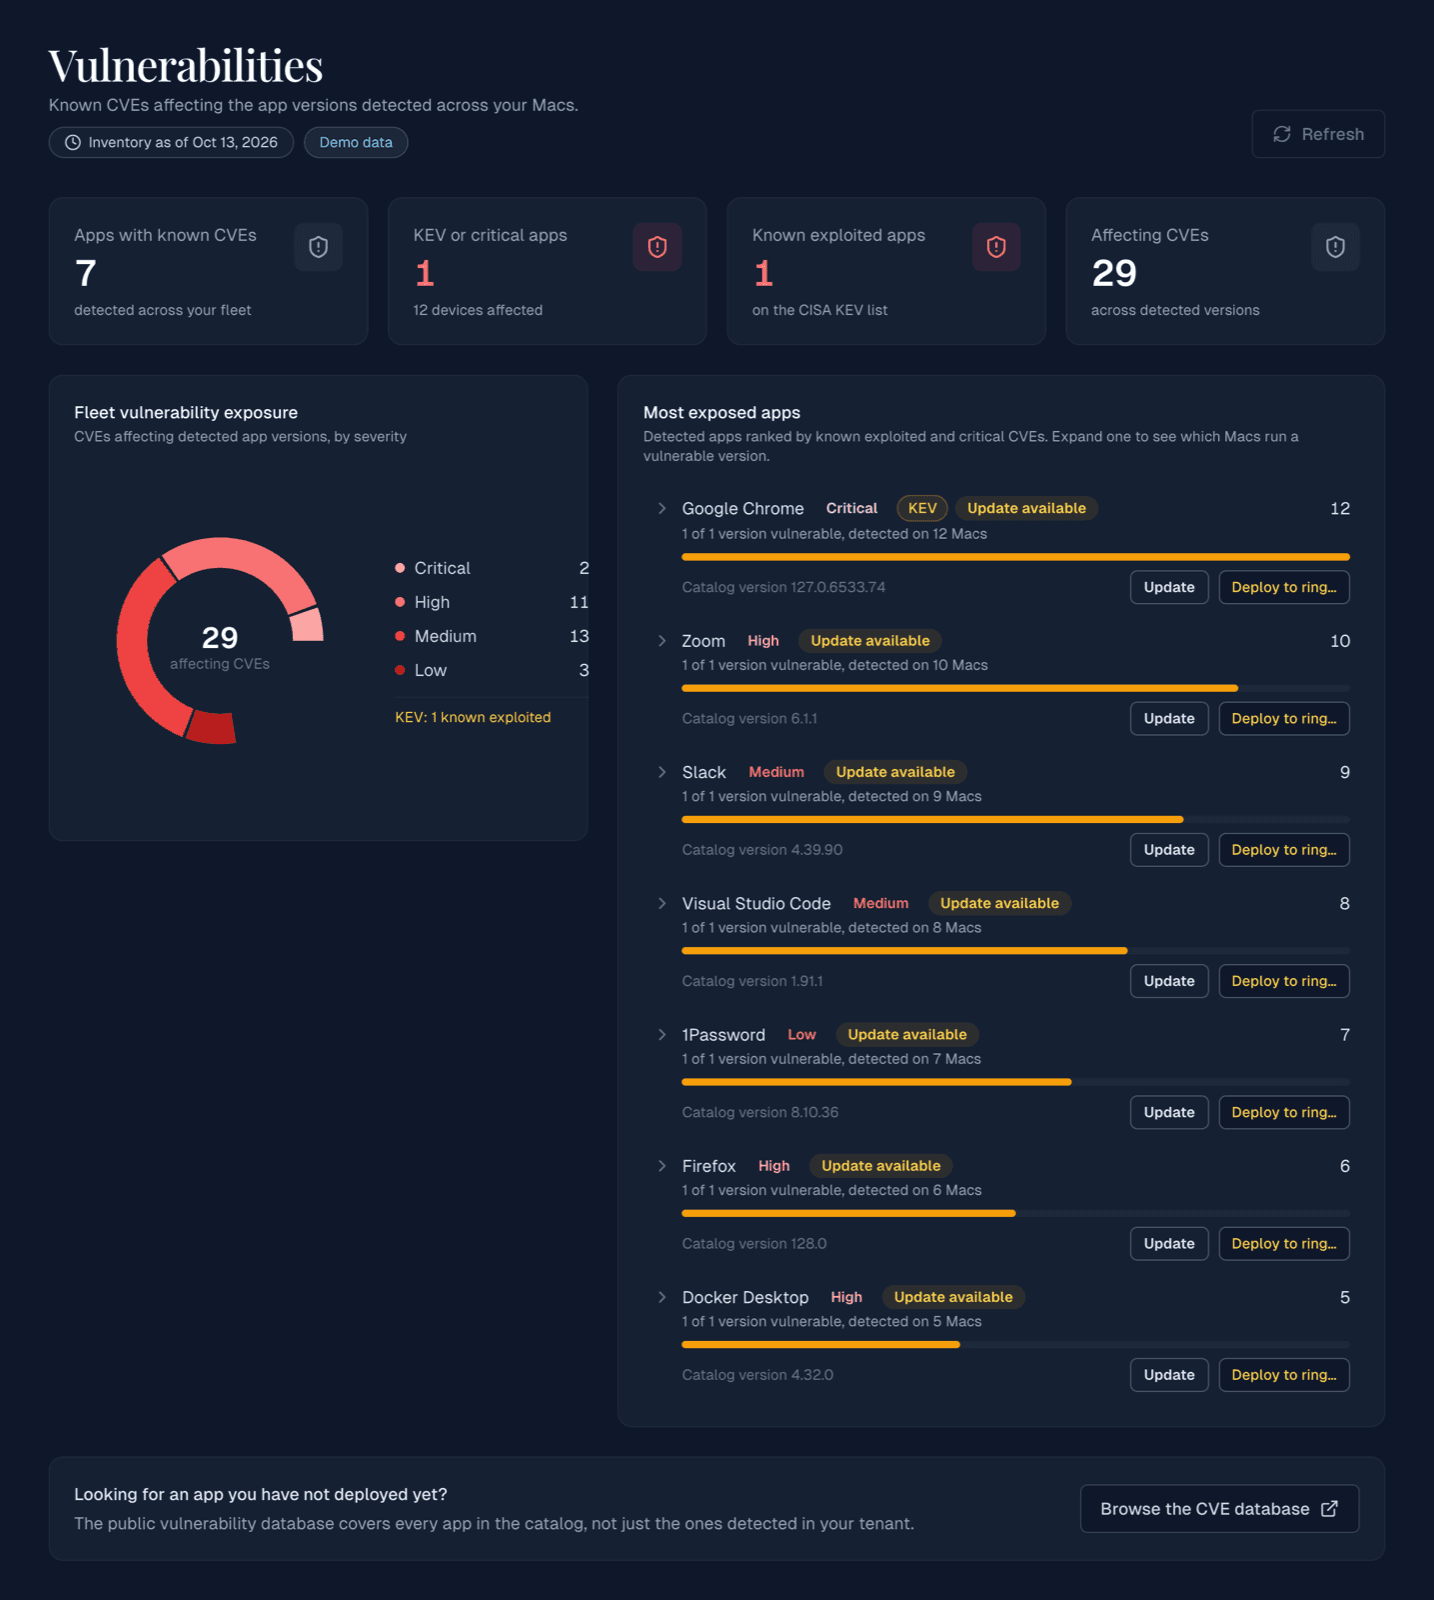
It uses the same device data as the dashboard, so it needs the same Grant access step the first time.
What you see
- Apps with known CVEs, KEV or critical apps, Known exploited apps, and Affecting CVEs across your detected versions.
- Fleet vulnerability exposure: the affecting vulnerabilities by severity.
- Most exposed apps: ranked by actively exploited and critical vulnerabilities. Expand an app to see which Macs run a vulnerable version.
Fix an exposed app
Select Update to publish the newest catalog version, or Deploy to ring… to send it to a pilot group first. A confirmation shows what will happen; assignments and old versions are handled according to your settings.
Viewers can see everything on this page but can't update.
Public vulnerability database
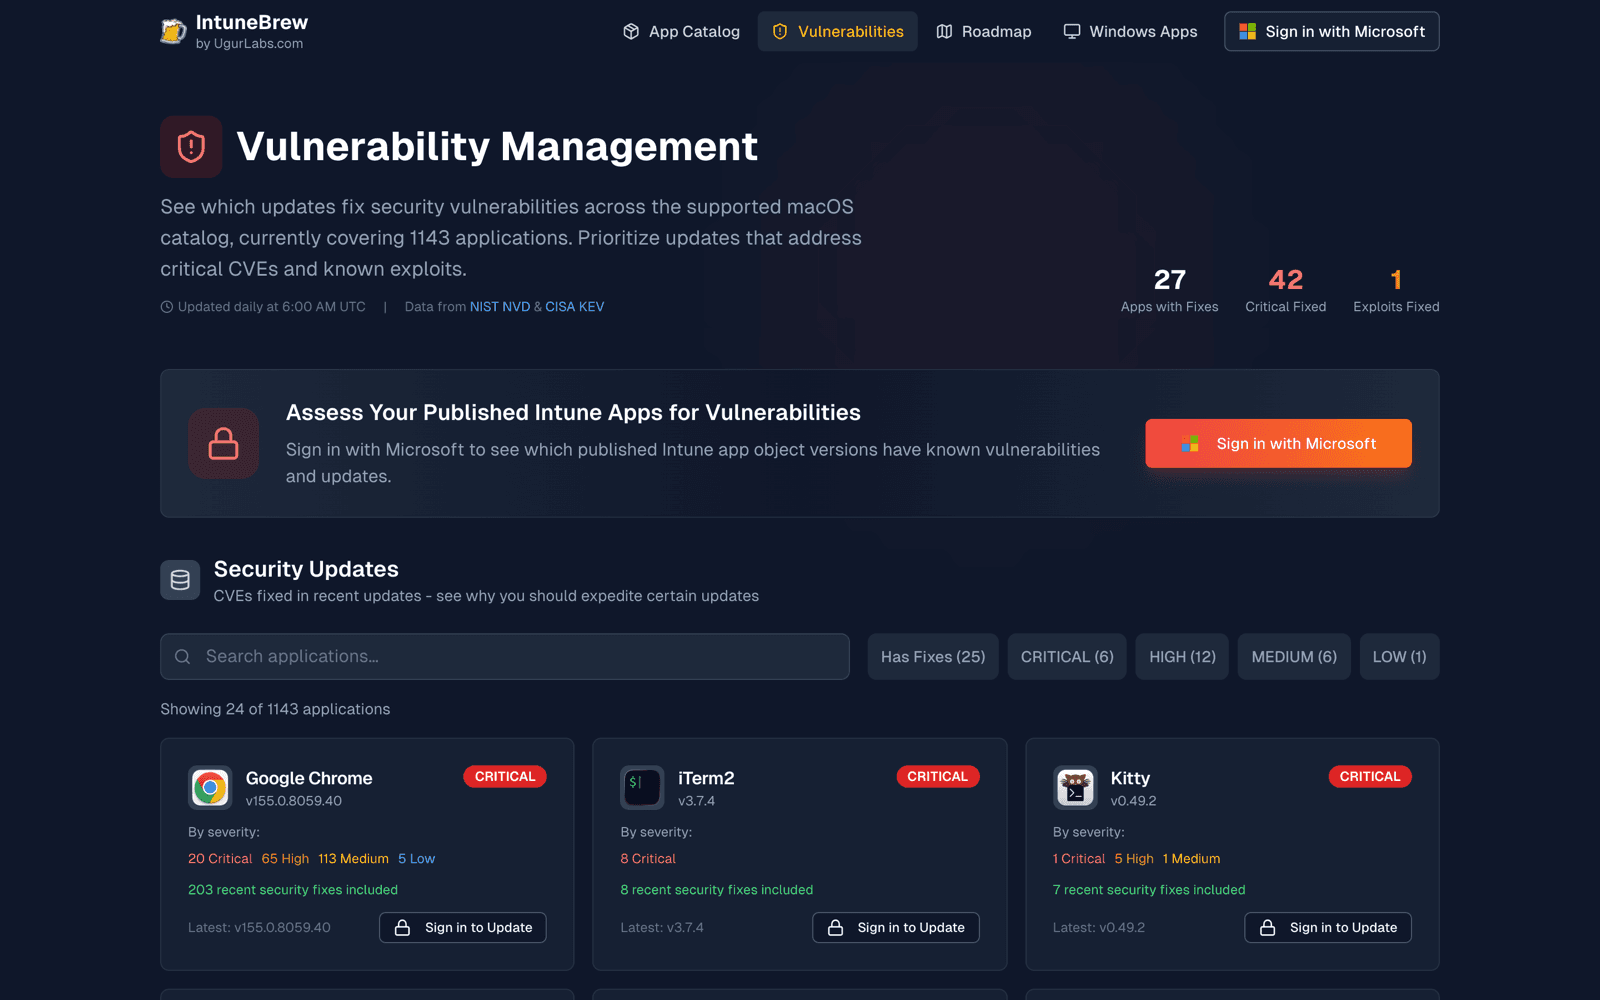
Anyone can browse vulnerability data for every catalog app at intunebrew.com/vulnerabilities, updated daily at 6:00 UTC. Filter by severity or by apps with fixes available.
Alerts
Turn on Known exploited vulnerability and Critical vulnerability under Notifications to get an email when such a vulnerability affects an app version deployed in your tenant.